We put our money where our mouth is. About $1,000 in Bitcoin sits in a fresh wallet. Its seed phrase was encrypted with Legacy, and the encrypted seed is published below for anyone in the world to download, study, and attack.
The only things we're keeping secret are the two keys — exactly what a real Legacy user keeps secret. Everything else is public: the ciphertext, the full protocol specification, the open-source code, and the test vectors. No secret algorithm, no security through obscurity. If Legacy has a weakness, this is your chance to prove it and get paid for it.
The target
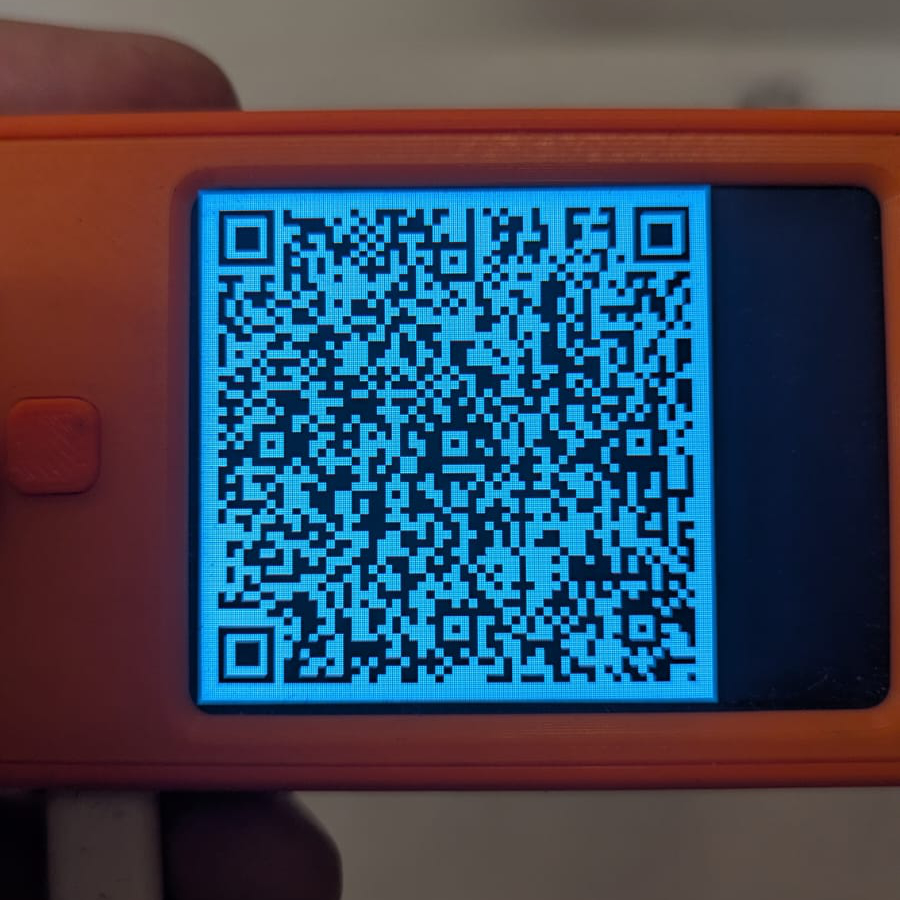
Encrypted seed (QR)
The encrypted seed as the SeedSigner displayed it. Scan it straight into Legacy.
Encrypted seed (text)
The same payload as text. This is the complete payload — nothing trimmed.
Bounty address
The first receive address of the wallet. Watch it on any block explorer: as long as the balance is there, the challenge is unbroken.
What you're up against
Legacy uses standard, battle-tested primitives straight from the browser's Web Crypto API.
Full details are in the protocol spec.
Two keys, both required
The seed was encrypted under a benefactor key and a beneficiary key, joined into a single password. You need both, exactly, to decrypt.
600,000 rounds of key stretching
The password goes through PBKDF2-HMAC-SHA256 with 600,000 iterations and a random 16-byte salt. Every single guess costs an attacker 600,000 hashes, and the salt makes precomputed tables useless.
AES-256-GCM
The seed is encrypted with AES-256-GCM, the same authenticated cipher that protects most of the world's HTTPS traffic. The ciphertext carries no header, no marker, and no fixed bytes — every visible character is random.
Strong, randomly chosen keys
The keys for this challenge were generated the way our Security guide recommends: multiple independent random words, no personal meaning, no relationship between the two. Profiling us won't help. That's the point: Legacy is as strong as the keys you choose, and these were chosen well.
Rules
- No sign-up, no entry fee, no purchase. Anyone can try. The payload is public.
- Winner takes it by sweeping it. If you decrypt the seed, the wallet is yours. Move the coins and you've won. No claim form, no permission needed.
- Wallet details: standard BIP-84 native SegWit (
m/84'/0'/0'), no BIP-39 passphrase. Your decrypted seed opens it directly in any wallet. - Attack the cryptography, not people. Phishing, social engineering, or breaking into anyone's devices or accounts is out of bounds — and illegal. This is a test of the protocol and the ciphertext only.
- Tell us how you did it. If you win, we'd love a write-up. A real flaw would get fixed and you'd get full credit (and bragging rights forever).
- No end date. The challenge runs until the coins move. We may add to the bounty over time; we will never remove it while the challenge is open.
Want to try?
Grab the open-source Legacy-offline.html or the online decrypt demo, paste the payload, and start guessing. Or write your own decryptor from the spec — it fits on one page.
And if you'd rather use Legacy than break it: this is exactly what your own encrypted seed looks like to the rest of the world. Read How It Works and the Security guide to set up your own inheritance plan.